


Risk Management
Policy
With the globalization of society, risks surrounding companies are becoming more diverse. The Anritsu Group recognizes that strengthening risk management is an extremely important management issue in order to continue its business and fulfill its responsibilities to society. Based on this idea, we have developed the Anritsu Group Risk Management Policy.
| Risk Management Policy |
|---|
The Anritsu Group will maintain and increase its corporate value, fulfill its corporate social responsibility and seek sustainable development for the Group by appropriately managing risks that affect management.
|
System
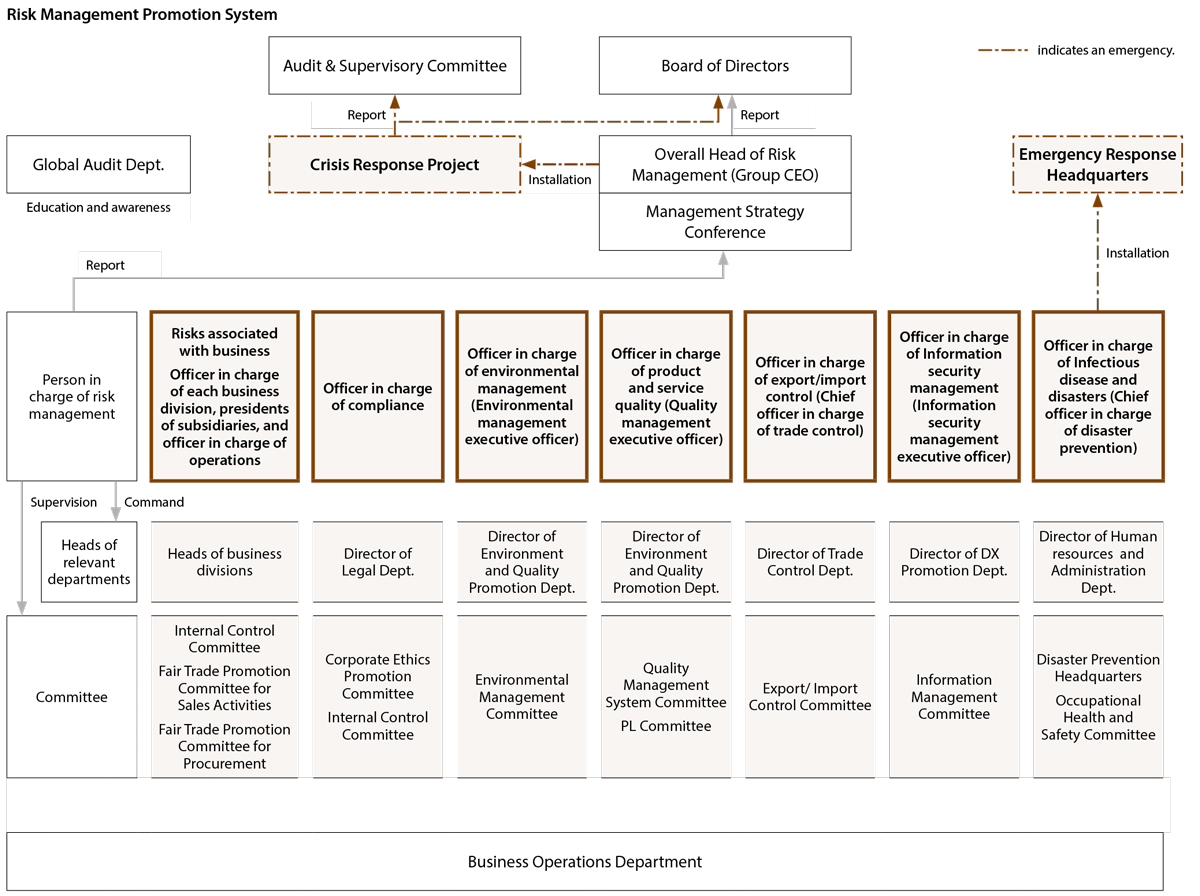
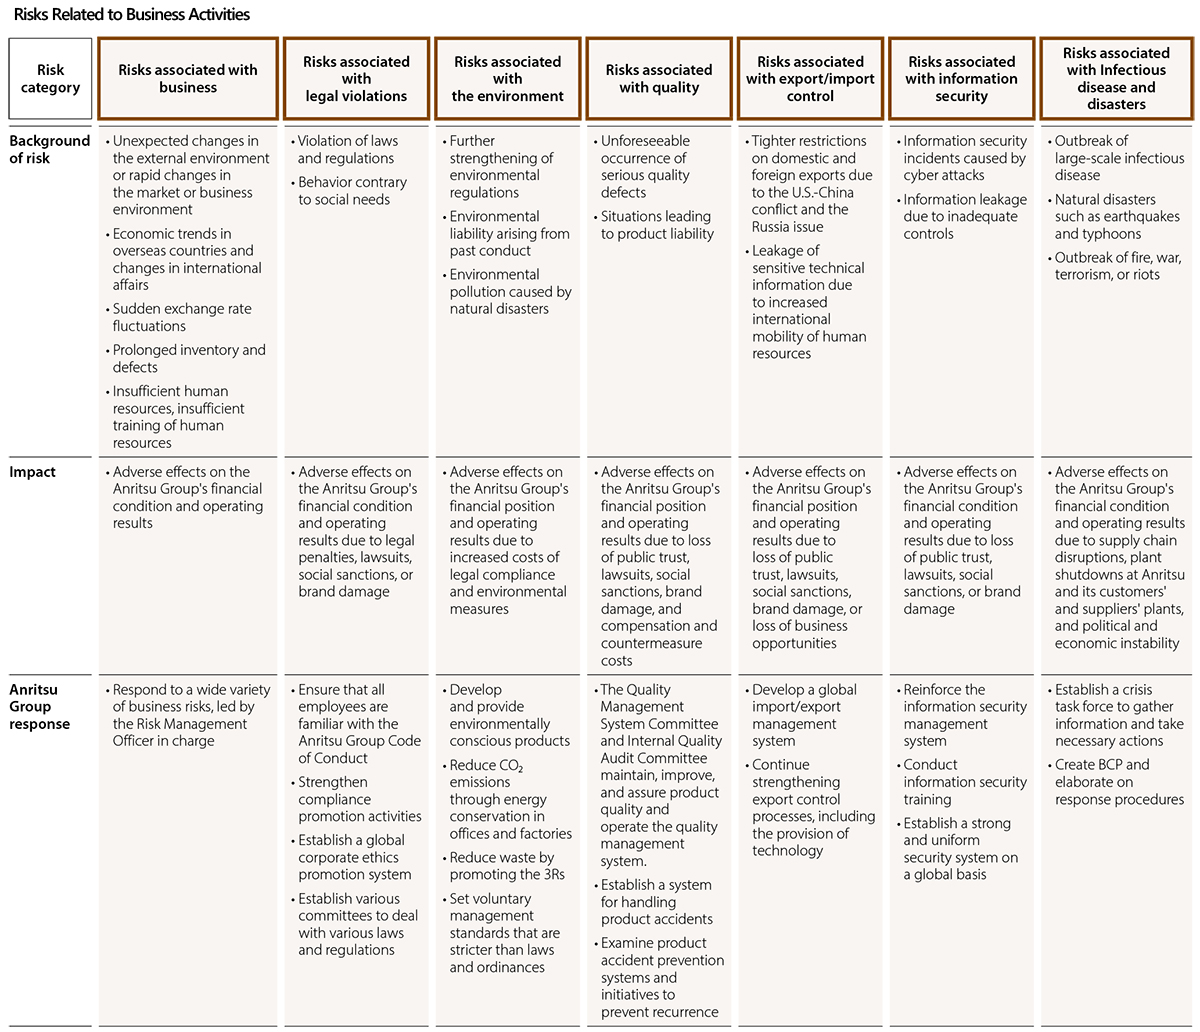
The Anritsu Group has established Basic Risk Management Regulations and classified major risks associated with business activities into seven categories: business risk, risk of legal violations, environmental risk, product and service quality risk, export and import control risk, information security risk, and infectious disease and disaster risk. These risk management activities are overseen by the Board of Directors, while the officer in charge of the relevant matters, under the supervision of the Group CEO, is responsible for risk management.
The person in charge of risk management directs the relevant departments to carry out committee activities. These committees conduct risk assessments, support the establishment of internal controls, and conduct audits. The person in charge of risk management reports the results of these activities to the Management Strategy Conference, which deliberates and evaluates them. Then, the Group CEO or the person in charge of risk management reports the results of these deliberations to the Board of Directors as necessary. Each person in charge of risk management supports the activities of overseas group companies in their respective fields. With regard to compliance risks, the head of each regional control company formulates an annual plan and conducts risk assessments.
Within the risk management system, the risk associated with legal violations is mainly investigated and analyzed for the risks related to the following laws and regulations. An activity plan is formulated each fiscal year and the results of these activities are reviewed in order to make improvements.
Major Laws and Regulations:
Labor laws, health and safety laws, subcontracting laws, anti-monopoly laws, premiums and representation laws, financial instruments and exchange laws, laws related to intellectual property, company laws, laws related to antibribery, laws related to human rights (such as modern slavery laws)
Activities and Achievements
Risk Management Training
The Risk Management Promotion Department holds workshop-style "Risk Management Training" for newly appointed managers in the domestic group. In FY2024, 31 out of 33 eligible participants took the course, for a participation rate of 94%. After learning specific risk management methods during training, participants will apply the techniques they have learned to their actual work, and then attend follow-up training six months later.
Training for overseas group companies focuses on the risk of fraud. In FY2024, we focused on creating practical e-learning teaching materials. In FY2025, the completed materials will be used to conduct training in an e-learning format.
Global Risk Management
Anritsu has established guidelines outlining the minimum requirements that the Anritsu Group must comply with in its management. The requirements cover a wide range of areas, from familiarization with company philosophy and codes of conduct to internal controls, compliance, respect for human rights, promotion of diversity, personnel management, and information security.
Overseas group companies conduct control self-assessment (CSA) based on these guidelines. CSA is conducted annually. The internal control department of each Anritsu company (business operation) uses the results to evaluate the level of control at each company and provides feedback on priority issues to be addressed. CSA began in FY2020, gradually expanding the scope of questions asked, and has evaluated all items in the guidelines since FY2022. In the FY2024 evaluation, it was confirmed that each company met the requirements and achieved a stable management level as a result of implementing countermeasures.